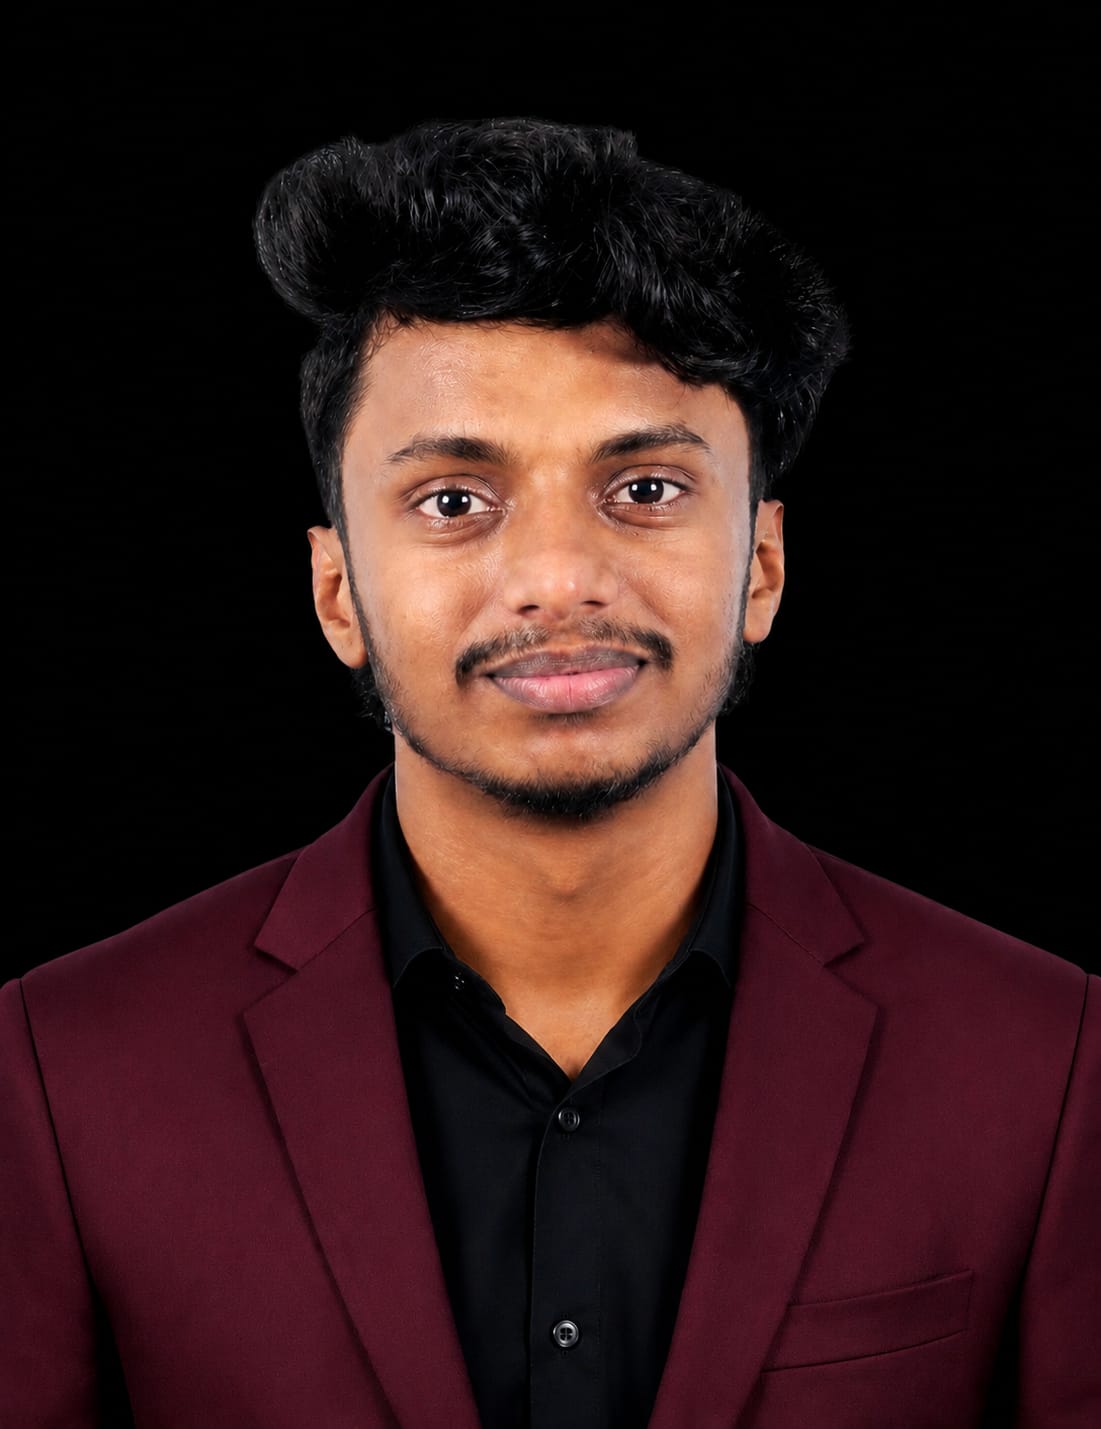
visitor@portfolio:~$ whoami
Securing networks, hunting threats, defending the perimeter.
visitor@portfolio:~$ cd ./about
> About
Recent B.E. Cybersecurity Engineering graduate from Paavai Engineering College, Namakkal, actively pursuing SOC Analyst and Blue Team roles in Chennai and Bangalore. Passionate about hands-on defensive security, log analysis and threat detection — building labs, breaking them, and then instrumenting them until nothing moves unseen.
- location:
- Tamil Nadu, India
- focus_area:
- SOC Ops · Blue Team · Threat Hunting
- status:
- Actively job hunting
- certifications:
- 4 + Wazuh Ambassador
visitor@portfolio:~$ cd ./education
> Education
[2022-11] > PROGRAM_STARTED — B.E. Cybersecurity
[institution] Paavai Engineering College, Namakkal
[2025] > RESEARCH_PUBLISHED — "Creating Tailored Detection and Prevention Mechanisms for Targeted Threats" (IJARIIT, Vol. 11)
[2026-05] > GRADUATED — status: exit code 0
visitor@portfolio:~$ cd ./experience
> Experience
[2026-01] > INTERNSHIP_STARTED
SOC Analyst Intern — The Mind IT
Jan 2026 – Apr 2026 · ~4 months
Triaged 40+ daily alerts in Splunk and Wazuh, investigated 30+ weekly anomalies via SPL and OSINT (AbuseIPDB, AlienVault OTX), escalated 15+ confirmed incidents within 15-minute SLAs, and reduced recurring false positives by ~25% via Wireshark & rule tuning.
[2026-04] > INTERNSHIP_COMPLETED
visitor@portfolio:~$ cd ./certifications
> Certifications
Certified SOC Analyst (CSA)
EC-Council
Ethical Hacking Essentials (EHE)
EC-Council
Splunk Core Certified User
Splunk
Certified CyberOps Associate
Cisco
Wazuh Ambassador
Wazuh (Certificate of Recognition)
visitor@portfolio:~$ cd ./skills
> Skills
# SIEM & Monitoring
# Network & Endpoint
# Threat Intelligence
# Frameworks
# Detection & Ops
# Soft Skills
visitor@portfolio:~$ cd ./projects
> Projects
CTI Automation Platform
Threat intel pipeline pulling indicators from AlienVault OTX, AbuseIPDB and URLhaus into Splunk.
AI-Powered SOC Alert Triage
Random Forest model that prioritises SOC alerts and reduces analyst fatigue.
Zero Trust Network Simulation Lab
Zero Trust network simulation: pfSense micro-segmentation, a Python policy engine and Wazuh-style alert correlation, following NIST SP 800-207.
visitor@portfolio:~$ cd ./contact
> Contact
- ibrahim.cybrx@gmail.com
- linkedin.com/in/mohamed-ibrahim-h-585b92282
- github.com/ibu-cyx0
- tryhackme.com/p/IbrahimCyb3r4
- Tamil Nadu, India · open to Chennai / Bangalore